CVE-2026-98432: Critical Linux Kernel Use-After-Free in IPv4 TCP — What It Is and How to Fix It

Futuristic server room network diagram showing a red failure spreading through blue system connections

CVE-2026-98432: Critical Linux Kernel Use-After-Free in IPv4 TCP — What It Is and How to Fix It

A critical vulnerability in the Linux kernel (CVE-2026-98432) has drawn significant attention. Rated 9.8 (Critical) by the Linux kernel CVE team and marked High priority by Ubuntu, it involves a use-after-free race condition in IPv4 TCP option handling.

As of late October 2026, fixed packages are available on several distributions including Debian, Oracle Linux, parts of Amazon Linux, openSUSE Leap 16.0, and SUSE Linux Micro 6.2. Ubuntu still lists supported releases as vulnerable with fixes in progress, while Red Hat has deferred its fix. A research demonstration (involving Anthropic’s Claude) reportedly produced a laboratory remote-root exploit under specific conditions, underscoring the need for prompt action once patches arrive.

What Is CVE-2026-98432?

The bug lives in the IPv4 TCP handshake code. When the kernel creates a new child socket from a request socket (tcp_v4_syn_recv_sock()), it transfers ownership of the IP options (ireq->ireq_opt → newinet->inet_opt) without copying them.

A concurrent CPU can process a retransmitted SYN for the same request socket and build a SYNACK (tcp_v4_send_synack() → ip_options_build()). Because the options are freed with a plain kfree() (no RCU grace period) when the child socket is destroyed, this creates a classic use-after-free. A related path exists with TCP request-socket migration (net.ipv4.tcp_migrate_req=1 or certain BPF programs).

IPv6 is largely unaffected by the primary issue (options are duplicated), though a similar migration problem exists for CALIPSO and is addressed separately.

The flaw has been present since roughly Linux 4.4. Upstream fixed it by switching to kfree_rcu() in the relevant destructors (commit e3f33b0a1d89...). Stable kernels that include the fix include 5.10.272, 5.15.223, 6.1.190, 6.6.159, 6.12.113, 6.18.56, 7.2.10, and mainline 7.3+.

Impact and Exploitability

  • Remote, unauthenticated network attack surface (TCP connections).
  • Potential outcomes: kernel crash / denial of service, memory corruption, or (in advanced cases) privilege escalation to root.
  • Winning the race is non-trivial, which is why some vendors score it lower (e.g., SUSE and Oracle 8.1, Red Hat ~5.9–8.1, Amazon 7.0). Ubuntu and the kernel CNA use the 9.8 score.
  • No confirmed widespread in-the-wild exploitation has been reported as of this writing, and it is not listed in CISA’s KEV catalog. However, a public research demonstration of a zero-click remote-root chain (particularly effective against multipath TCP listeners) raises the urgency.

Any system accepting TCP connections on a vulnerable kernel is potentially exposed—servers, cloud instances, containers sharing the host kernel, etc.

Current Status (as of 29 October 2026)

DistributionStatusNotes / Fixed Version
Ubuntu 22.04 / 24.04 / 26.04 / 26.10Vulnerable – fix in progressTarget versions exist but not yet released
Ubuntu 16.04 / 18.04 / 20.04VulnerableNo fix date announced
Debian 12 (bookworm) / 13 (trixie)Fixed6.1.190-1 / 6.12.113-1
Oracle Linux (UEK)FixedMultiple ELSA advisories
Amazon Linux 2023 (some kernels)Partially fixedkernel 6.18 and 6.12 fixed; others pending
openSUSE Leap 16.0Fixedkernel 6.12.0-160000.40.1 or later
SUSE Linux Micro 6.2Fixedkernel 6.12.0-160000.40.1 or later
SLES 15 SP4–SP6 LTSS / SLES 16.0Fixed or in progressSee SUSE advisories (e.g. SUSE-SU-2026:24386-1)
RHEL 8/9/10 + OpenShiftFix deferredNo released packages yet

Always check the official trackers (Ubuntu CVE page, SUSE CVE page, etc.) for the latest package status, as this changes quickly.

How to Check If You Are Affected

  1. Identify your running kernel: uname -r
  2. On Ubuntu: dpkg -l | grep linux-imageThen match against https://ubuntu.com/security/CVE-2026-98432.
  3. On openSUSE / SUSE: rpm -q kernel-default # or zypper se -s kernel-defaultCompare against the fixed version (e.g. 6.12.0-160000.40.1+).
  4. Monitor for available updates on your distribution.

Steps to Fix the Vulnerability

Primary fix: Install the patched kernel and reboot.

On Ubuntu (once packages are published)

sudo apt update
sudo apt full-upgrade
sudo reboot

On Debian

sudo apt update
sudo apt full-upgrade
sudo reboot

On openSUSE Leap / SUSE Linux Enterprise / SUSE Linux Micro

sudo zypper refresh
sudo zypper update
# or more specifically:
sudo zypper in -t patch openSUSE-...   # follow the exact patch name from the advisory
# or
sudo zypper up kernel-default
sudo reboot

For openSUSE Leap 16.0 and SUSE Linux Micro 6.2 the fixed kernel is 6.12.0-160000.40.1 (or later). After updating, confirm with uname -r.

On RHEL / AlmaLinux / Rocky / Oracle (when available)

sudo dnf update kernel
sudo reboot

Important: The vulnerability is fixed only after the system is running the patched kernel. Simply installing the package is not enough—reboot is mandatory.

Temporary Mitigations (While Waiting for Patches)

These reduce attack surface but do not fully eliminate the primary race:

  • Disable TCP request-socket migration: sudo sysctl -w net.ipv4.tcp_migrate_req=0Make it persistent by adding the line to /etc/sysctl.d/99-tcp-migrate.conf (or similar) and running sysctl --system.
  • Limit exposure of TCP services to untrusted networks (firewall rules, security groups, reverse proxies).
  • Prefer IPv6-only listeners where feasible (the primary path is IPv4-specific).
  • Avoid enabling multipath TCP (MPTCP) on publicly reachable services if not required.

These are stop-gaps only. The real solution is the kernel update.

Best Practices Going Forward

  • Subscribe to your distribution’s security notices (Ubuntu USN, SUSE Security Advisories, etc.).
  • Enable automatic security updates where appropriate, but treat kernel updates carefully (test first in non-production).
  • Maintain an inventory of kernel versions across your fleet (especially cloud instances and containers).
  • For high-security environments, consider live-patching solutions once they support this CVE, though a full reboot remains the cleanest approach for kernel fixes of this type.

Conclusion

CVE-2026-98432 is a serious race-condition use-after-free in a core networking path. While reliable remote exploitation is non-trivial, the combination of a 9.8 CVSS score, network reachability without authentication, and demonstrated research exploits makes it high priority.

Monitor the official trackers closely. As soon as fixed kernel packages appear for your release (already available for openSUSE Leap 16.0, SUSE Linux Micro 6.2, Debian, and Oracle), install them and reboot. Until then, apply the temporary mitigations and restrict network exposure.

Stay patched, stay safe.
PHP2Shell: Critical PHP Remote Code Execution Vulnerabilities Require Immediate Action

phpshell

PHP2Shell: Critical PHP Remote Code Execution Vulnerabilities Require Immediate Action

phpshell

The PHP community has released emergency security updates to address two critical remote code execution vulnerabilities, CVE-2026-109618 and CVE-2026-109619, collectively being referred to as PHP2Shell. Both vulnerabilities can allow an unauthenticated attacker to execute code on affected web servers through specially crafted HTTP requests. PHP has rated both vulnerabilities as 9.2 (Critical) and administrators should patch immediately. [almalinux.org], [almalinux.org]

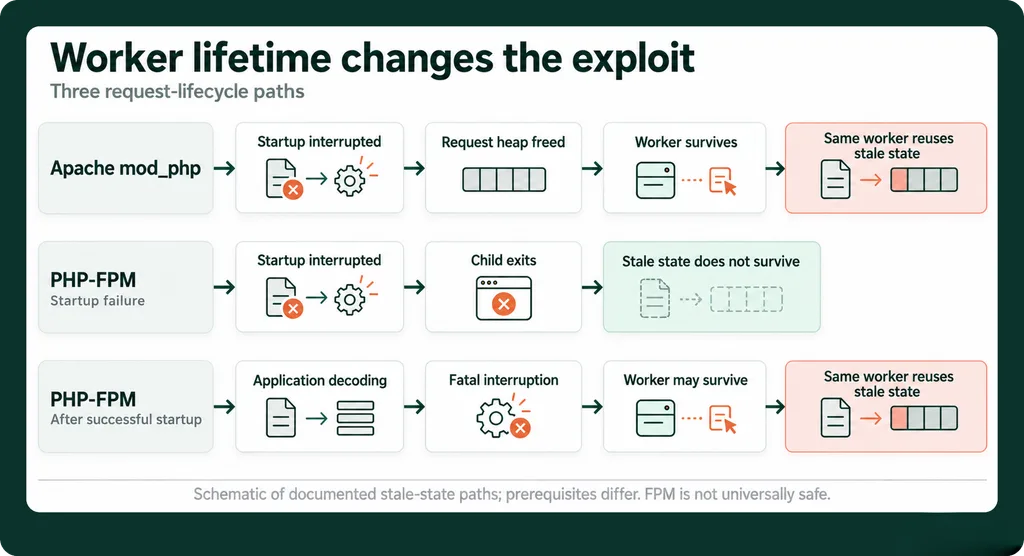
The vulnerabilities affect multiple PHP versions and deployment methods, including PHP-FPM, Apache mod_php, CGI, LiteSpeed, and FrankenPHP installations. PHP released fixed versions on October 21, 2026, with updates available in:

  • PHP 8.2.35
  • PHP 8.3.36
  • PHP 8.4.27
  • PHP 8.5.12

[almalinux.org], [phpvulnera…lities.app]

ViciBox 11 and ViciBox 12

The ViciDial team has already published fixes for supported ViciBox releases.

ViciBox 11

Documentation:

Update commands:

zypper ref
zypper dup --from openSUSE-Leap-15.5-ViciDial-ViciBox --allow-vendor-change
systemctl restart apache2

After updating, verify PHP:

php -v

You should see:

PHP 7.4.34-dev

ViciBox 12

Documentation:

Update commands:

zypper ar https://download.opensuse.org/repositories/devel:/languages:/php:/php82/openSUSE_Leap_15.6/devel:languages:php:php82.repo
zypper mr -f devel_languages_php_php82
zypper --gpg-auto-import-keys ref
zypper dup --from devel_languages_php_php82 --allow-vendor-change
systemctl restart apache2

After updating, verify PHP:

php -v

You should see:

PHP 8.2.35 or later.

Important Note for ViciBox 11 Users

The ViciDial team has indicated that it is becoming increasingly difficult to maintain and build packages for the aging ViciBox 11 platform. Administrators still running ViciBox 11 or older should begin planning an upgrade path, as older openSUSE repositories may eventually be removed from public mirrors.


AlmaLinux Fix

AlmaLinux has released patched PHP packages for all supported PHP streams across AlmaLinux 8, 9, and 10. The AlmaLinux project confirmed that patched packages are now available in the production repositories. [almalinux.org]

To update:

sudo dnf clean metadata
sudo dnf upgrade 'php*'

Restart PHP-FPM:

sudo systemctl restart php-fpm

If you are using Apache with mod_php:

sudo systemctl restart httpd

Verify the installed version:

php -v

For systems running PHP 8.2, the patched version should be:

PHP 8.2.35

or newer. AlmaLinux has also backported protections for some older, end-of-life streams where possible. [almalinux.org], [computingf…rgeeks.com]


Rocky Linux Fix

Rocky Linux administrators can patch affected systems using the standard AppStream update process. Updated packages have been synchronized from Red Hat’s security advisories for supported PHP streams. [computingf…rgeeks.com]

Update PHP:

sudo dnf upgrade 'php*'

Restart services:

sudo systemctl restart php-fpm
sudo systemctl restart httpd

Verify:

php -v

Supported streams should be updated to patched package releases, including PHP 8.2.35 and PHP 8.3.36 where applicable. [computingf…rgeeks.com], [php2shell.app]


Special Notice for VICIdial Servers Running PHP 7.4

Many older VICIdial deployments on AlmaLinux 8, Rocky Linux 8, and ViciBox 11 continue to use PHP 7.4. While the upstream PHP project no longer maintains the 7.4 branch, several distributions have backported security fixes to their packaged versions. The PHP2Shell vulnerabilities have been patched in supported vendor repositories even though the version number may still report as PHP 7.4.x. Administrators should not assume they are protected simply because they are running PHP 7.4 and should verify that all available operating system updates have been installed. [computingf…rgeeks.com], [php2shell.app]

AlmaLinux PHP 7.4

Update all PHP packages:

sudo dnf clean all
sudo dnf upgrade 'php*'
sudo systemctl restart httpd

Verify installed packages:

rpm -q php-common
php -v

AlmaLinux has released patched packages for PHP 7.4 in its repositories, including backported fixes for the PHP2Shell vulnerabilities. [computingf…rgeeks.com], [almalinux.org]

Rocky Linux PHP 7.4

Update all PHP packages:

sudo dnf clean all
sudo dnf upgrade 'php*'
sudo systemctl restart httpd

Verify package versions:

rpm -q php-common
php -v

Rocky Linux has synchronized the corresponding security updates from Red Hat for supported PHP 7.4 streams. Because Red Hat backports security fixes, the displayed version number may not change significantly even though the vulnerability has been patched. Administrators should review package changelogs and installed RPM versions rather than relying solely on php -v. [computingf…rgeeks.com], [php2shell.app]

Verify Your System Is Patched

After updating, verify your installed PHP packages:

rpm -q php-common

Or review the package changelog:

rpm -q --changelog php-common | grep CVE

If your repository updates are current and the CVE references appear in the changelog, the PHP2Shell fixes have been applied even if the PHP version string still shows 7.4. [php2shell.app]


IMPORTANT: PHP 7.4 is officially end-of-life upstream. While AlmaLinux, Rocky Linux, and ViciBox may provide backported security fixes, organizations should develop a migration plan to PHP 8.2 or newer as soon as practical for long-term security and support. [computingf…rgeeks.com], [almalinux.org]


What Administrators Should Do Right Now

  1. Identify all servers running PHP.
  2. Update PHP packages immediately.
  3. Restart PHP-FPM and/or Apache after patching.
  4. Verify the running version.
  5. Review logs for suspicious requests dating back to October 2026.
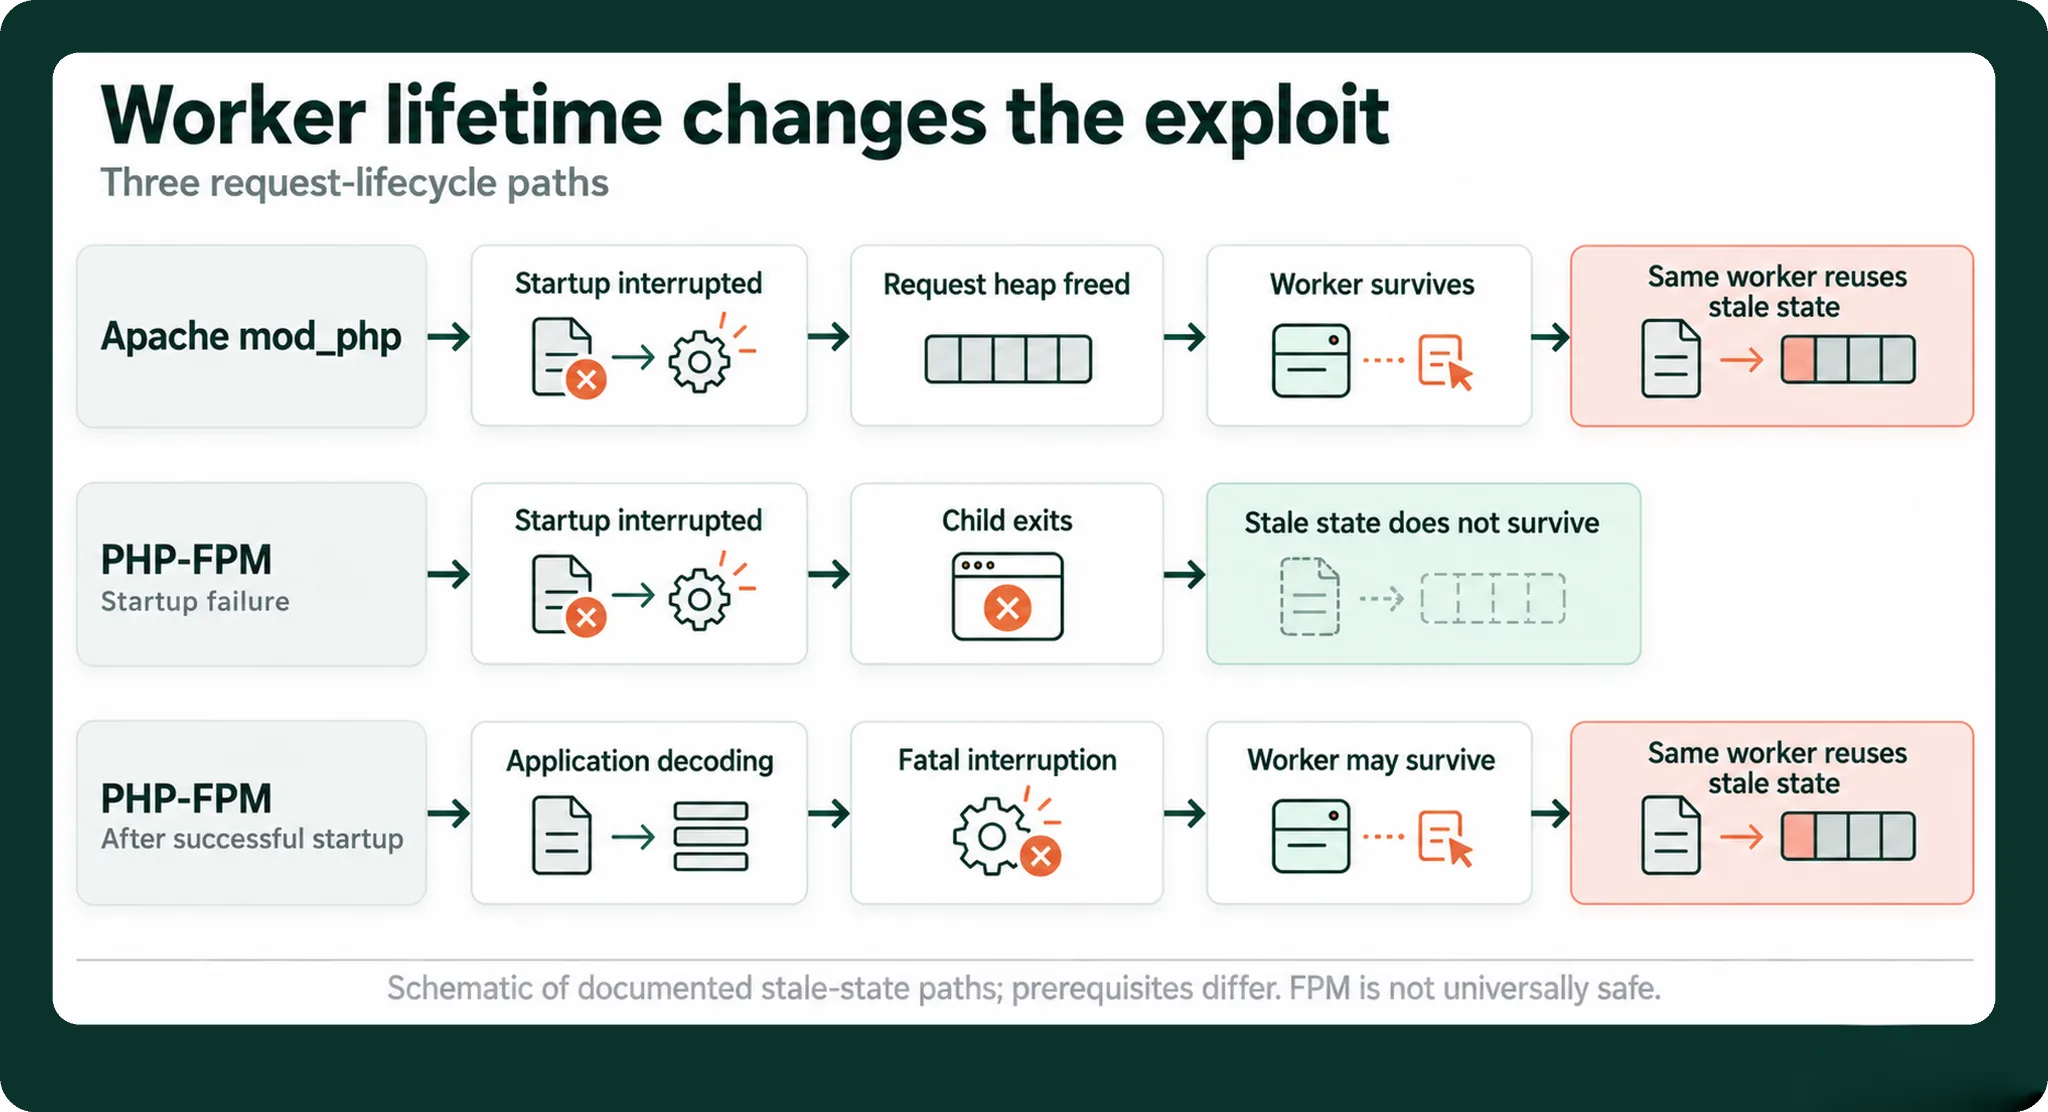
  6. Prioritize systems using Apache mod_php, as PHP developers have identified them as the highest-risk deployment model. [hackread.com], [notebookcheck.net]

Final Thoughts

Unlike vulnerabilities that affect a specific CMS or plugin, PHP2Shell targets the PHP runtime itself. This means WordPress, Laravel, Drupal, Joomla, VICIdial, custom applications, and virtually any PHP-powered application may be exposed if the underlying PHP installation remains unpatched. The safest course of action is simple: update PHP immediately and verify that your services have restarted successfully. [almalinux.org], [phpvulnera…lities.app]

Chris aka carpenox

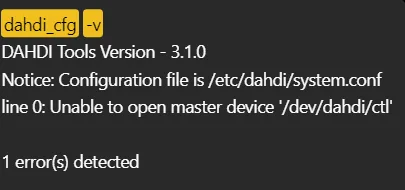
How to – Fix: Unable to open master device ‘/dev/dahdi/ctl’ for Dahdi

dahdi error

How to – Fix: Unable to open master device ‘/dev/dahdi/ctl’ for Dahdi

This happens after updating your operating system for redhat distro’s such as Alma, Rocky or CentOS. Its an easy fix thats outlined below:

Step 1 – Browse to proper directory

cd /usr/src/dahdi-linux-complete-3.4.0+3.4.0/

Step 2 – Recompile Dahdi

make && make install && modprobe dahdi

That’s all there is to it.

Introducing the New and Improved Full White Label Theme for ViciDial 2025 Edition by CyburDial

Agent 2025

Introducing the New and Improved Full White Label Theme for ViciDial 2025 Edition by CyburDial

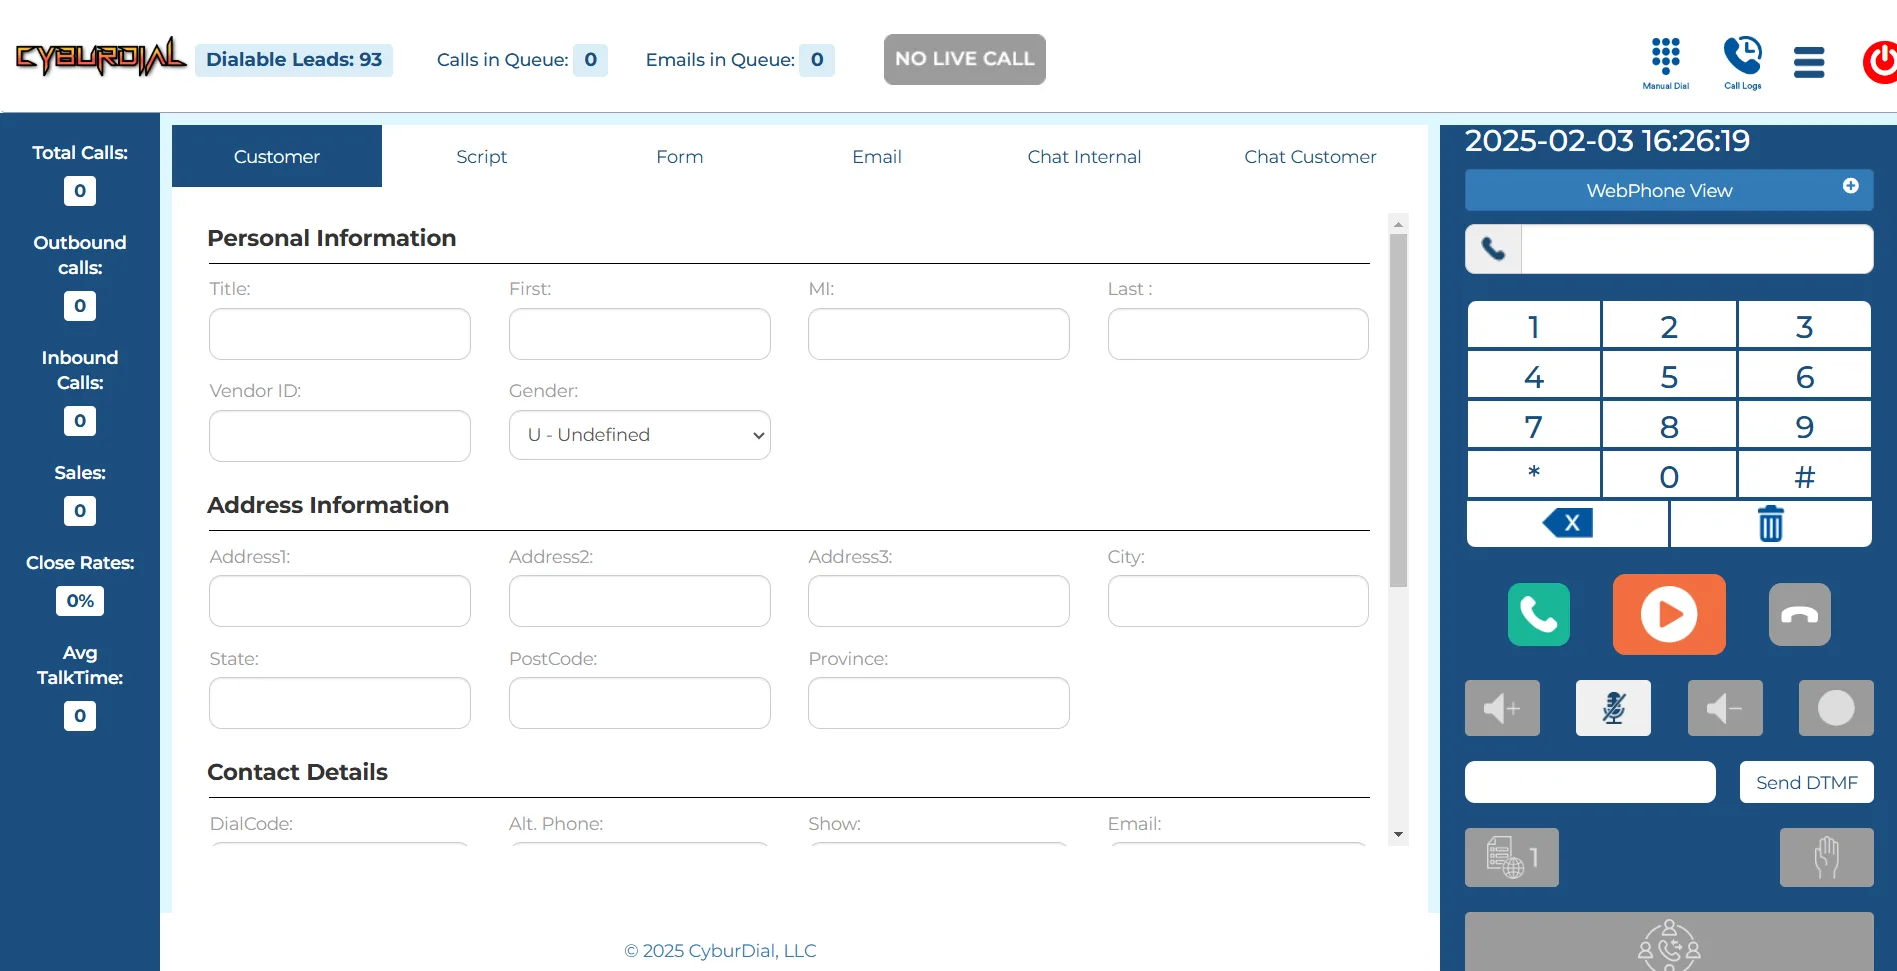
CyburDial is excited to announce the release of the 2025 edition of its Full White Label Theme for ViciDial! This latest version brings a host of new features and improvements designed to enhance the user experience for call center agents and administrators alike.

image 101361114 15620149

Enhanced Agent Screen Features

  • admin-melon
  • admin-green
  • Admin-dark-2
  • white admin

The new theme introduces several key features on the agent screen, including:

  • Disable Leads: Agents can now disable leads directly from the interface, streamlining the workflow and improving efficiency.
  • Manual Dial Buttons: The addition of manual dial buttons allows agents to have more control over their dialing process, ensuring they can handle calls more effectively.
  • More Customization Options: Agents can now customize their interface to better suit their individual preferences and working styles.
Agent 2025
Agent 2025
image 101361114 14092462

Bug Fixes and Interface Improvements

Over the past year, CyburDial has diligently worked on addressing bugs and improving the overall interface of ViciDial. These enhancements include:

  • Resolved Bugs: Numerous bugs reported by users have been fixed, ensuring a smoother and more reliable experience.
  • Interface Updates: The interface has been updated to be more intuitive and user-friendly, making it easier for agents to navigate and perform their tasks.

Added Support for Foreign Languages

Recognizing the global reach of ViciDial, the 2025 edition now includes support for additional foreign languages. This makes it easier for call centers around the world to use ViciDial in their native languages, improving communication and efficiency.

image

Try It Out Today

To learn more about the new and improved Full White Label Theme for ViciDial 2025 edition, visit our website: https://dialer.one/index.php/product/white-label-cyburdial-theme-2025/.

We look forward to seeing how this new edition helps your call center achieve even greater success!

How to – Fix ViciBox 11 and 12 errors

yast firewall

How to – Fix ViciBox 11 and 12 errors


Step 1 – Fix Apache errors if they exist

cd /etc/apache2/conf.d/
for file in *.conf.old; do mv "$file" "${file%.conf.old}.conf"; done
Answer y to all replace file questions

Step 2 – Recreate missing files


cd /usr/src/astguiclient/trunk
perl install.pl --copy_sample_conf_files --no-prompt

Step 3 – Rebuild missing directories

rm -rf /var/lib/asterisk/sounds
ln -s /usr/share/asterisk/firmware /var/lib/asterisk/firmware
ln -s /usr/share/asterisk/images /var/lib/asterisk/images
ln -s /usr/share/asterisk/moh /var/lib/asterisk/moh
ln -s /usr/share/asterisk/mohmp3 /var/lib/asterisk/moh
ln -s /usr/share/asterisk/sounds /var/lib/asterisk/sounds
ln -s /usr/share/asterisk/static-http /var/lib/asterisk/static-http
ln -s /usr/share/asterisk/phoneprov /var/lib/asterisk/phoneprov
ln -s /var/lib/asterisk/agi-bin /usr/share/asterisk/agi-bin
ln -s /var/lib/asterisk/phoneprov /usr/share/asterisk/phoneprov

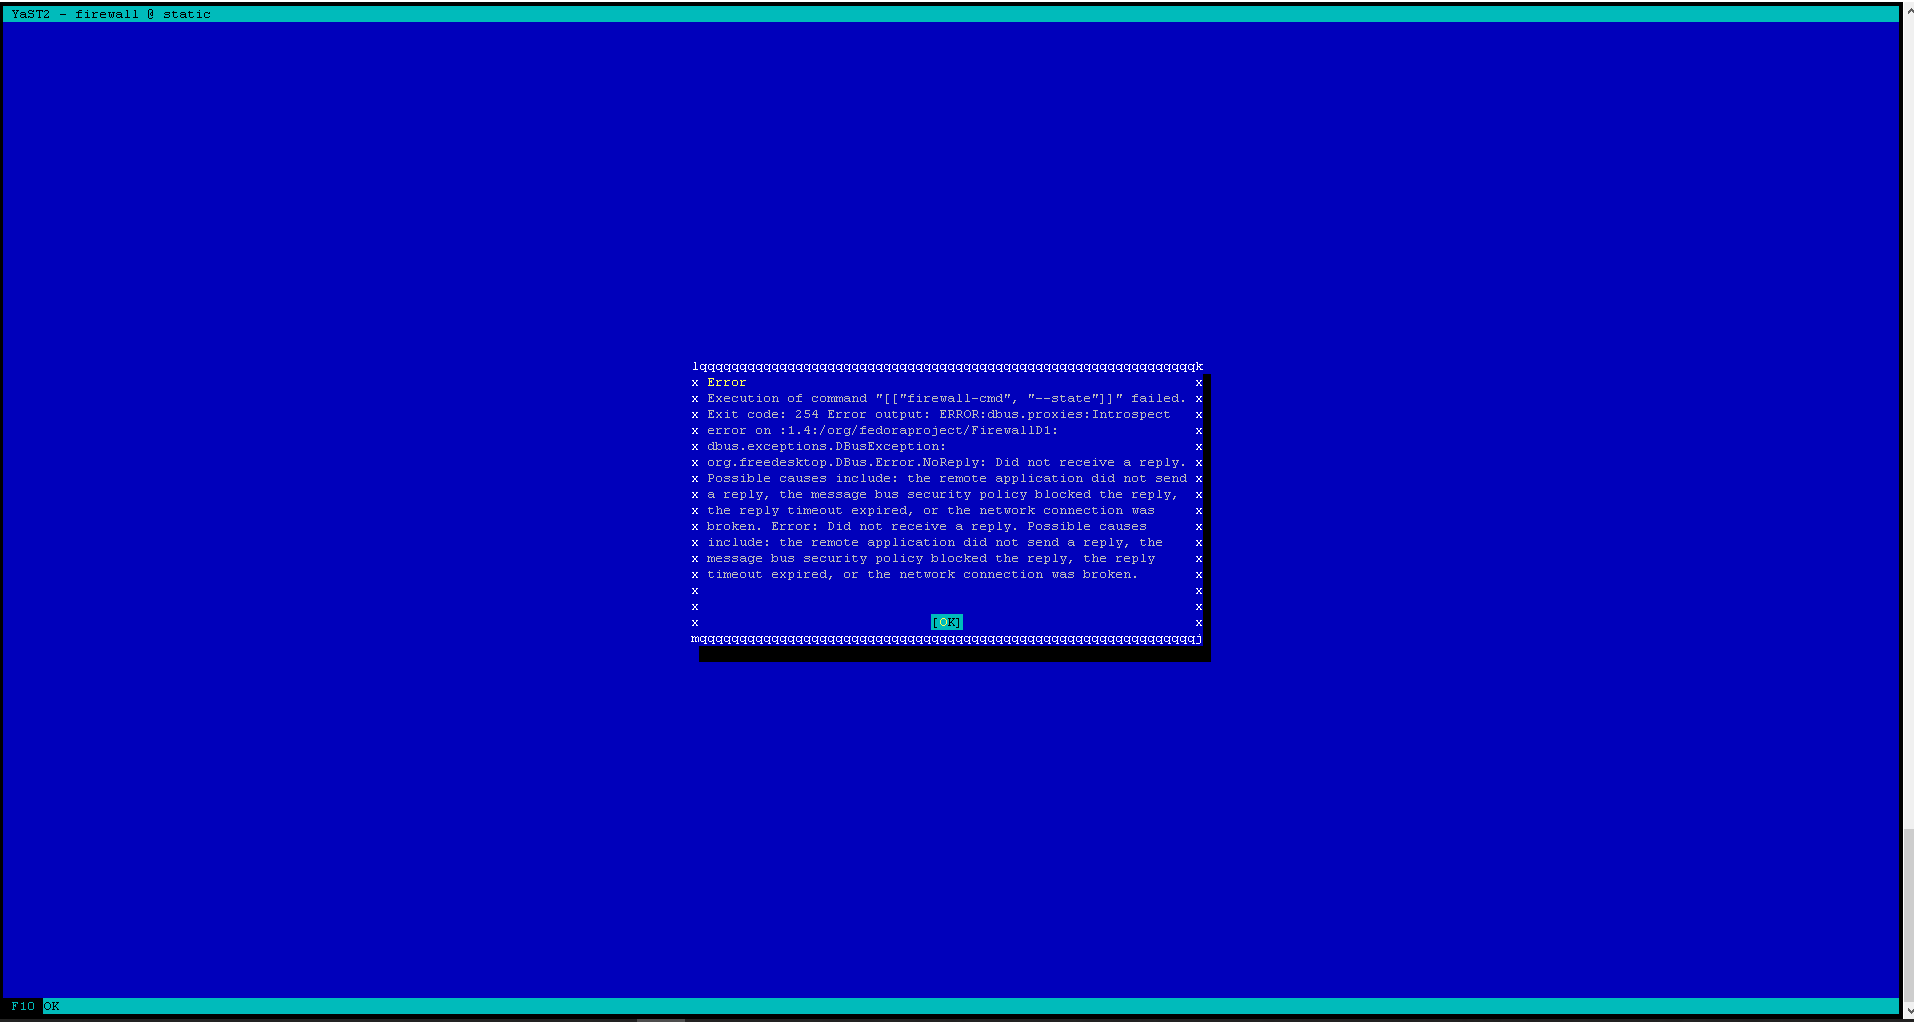
Step 4 – Fix yast (ViciBox 12 only)

yast firewall
zypper ref && zypper up
cp /etc/firewalld/zones/external.xml.rpmnew /etc/firewalld/zones/external.xml

Also apply this patch:
zypper in -t patch openSUSE-SLE-15.6-2024-4321=1 SUSE-2024-4321=1

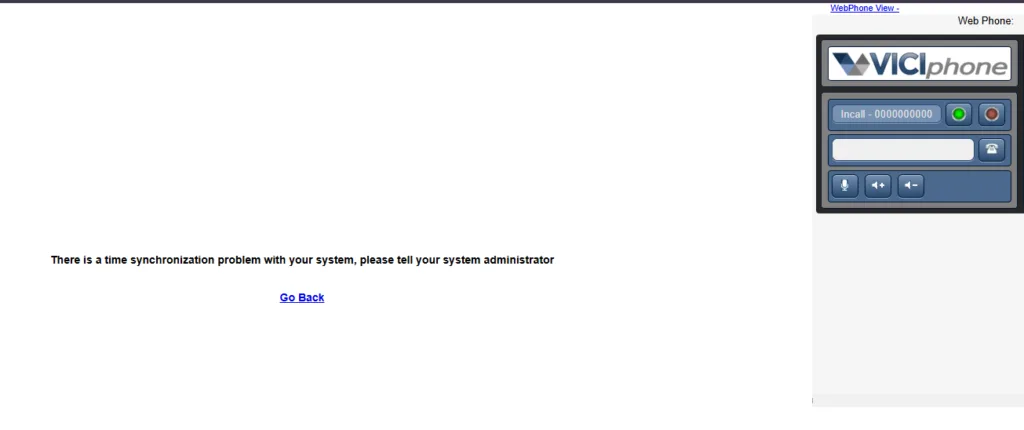
Time Sync Has been fixed in SVN 3905 and above

image 3

The last issue I have received reports about is a time synchronization issue even when times match everywhere on the system, I am working on debugging this currently, check back here for solution.

The fix is below:

echo "explicit_defaults_for_timestamp = Off" >> /etc/my.cnf.d/general.cnf
systemctl restart mariadb.service

Here is the documentation for it: https://docs.vicibox.com/en/latest/bugfix/bugfix1201-2.html


Here is also a link to the official docs from the ViciBox support website:

https://docs.vicibox.com/en/latest/bugfixerrata.html


Dynportal not working

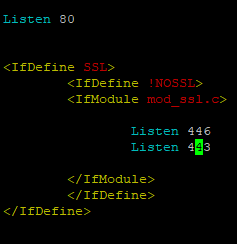
You need to add port 446 to /etc/apache2/conf/listen.conf as shown below:

image 10

If you have any questions feel free to join our discord: https://discord.gg/ymGZJvF6hK

Chris aka carpenox

Custom VICIdial Reports on GitHub

Custom Reports

Custom VICIdial Reports on GitHub

Introducing My New GitHub Repository for Custom VICIdial Reports

image 101361114 14092462

Hey there, fellow VICIdial enthusiasts!

I am thrilled to announce the launch of my latest GitHub repository, dedicated to creating custom reports for VICIdial. As a long-time user and developer in the VICIdial community, I understand the importance of having detailed and actionable data at your fingertips. This repository aims to enhance your call center’s efficiency and decision-making process by providing insightful reports tailored to your specific needs.

First Report: Area Code Call Breakdown

The first report available in this repository is the “Area Code Call Breakdown.” This report is designed to give you a comprehensive analysis of the number of calls made to each area code within a specified date range. Whether you are looking to optimize your outbound campaigns or ensure compliance with call regulations, this report will provide valuable insights into your call distribution patterns.

Understanding the New Spam Math for 2025

In light of recent changes to spam regulations, it is crucial to manage your Direct Inward Dial (DID) numbers effectively. According to the new guidelines for 2025, you should aim to keep the number of calls per DID below 50 calls per day. This report will help you achieve that by suggesting the optimal number of DIDs you should have for each area code based on the collected data and a six-day work week.

image png
image 101361114 15620149

Here’s how the calculations work:

  1. Total Calls to Area Code (per date range): This is the total number of calls made to a particular area code within your specified date range.
  2. Daily Call Volume: Divide the total calls by the number of days in the date range to get the average daily call volume.
  3. Required DIDs: To ensure each DID handles fewer than 50 calls per day, divide the daily call volume by 50 and round up to the nearest whole number.

For example, if you made 3,000 calls to area code 305 over a six-day period:

  • Daily Call Volume: 3,000 calls / 6 days = 500 calls per day
  • Required DIDs: 500 calls per day / 50 calls per DID per day = 10 DIDs

Exporting Data to CSV

To make the data even more accessible, this report includes the option to export your findings to a CSV file. This feature allows you to easily share the data with your team, analyze it in spreadsheet software, or integrate it with other systems for further processing.

image 1 png

Get Started Today

Ready to enhance your VICIdial reporting capabilities? Head over to my GitHub repository here to get started. You’ll find detailed instructions on how to set up and run the reports, as well as ongoing updates and new features.

Installation

Go to your “vicidial” directory on your web server. For ViciBox type “cd /srv/www/htdocs/vicidial” and for Redhat(Alma/Rocky/CentOS) type “cd /var/www/html/vicidial” and then clone the repo by typing:

git clone https://github.com/carpenox/Reports.git

Then browse to your server – https://yourserver.com/vicidial/Reports/did_report.php


I have added a bunch more that are all described on the github, but the latest one looks like this:

Record Search

Thats it, enjoy!

Stay tuned for more custom reports and features coming soon. If you have any suggestions or feedback, feel free to open an issue on GitHub or reach out to me directly on Discord: https://discord.gg/ymGZJvF6hK

Happy dialing!

Chris aka carpenox


Contabo opens DC in Singapore

How to – Fix Apache not starting on ViciBox

Artificial intelligence

How to – Fix Apache not starting on ViciBox

Contabo opens DC in Singapore

There is a new issue with ViciBox 9, 10 or 11 where Apache will not start up after installations. The error message is calling for mod_deflate which seems to not be there. The easy fix for this is to delete the include for it.

nano /etc/apache2/vhosts.d/dynportal.conf - Then go to line 16 and delete "Include /etc/apache2/conf.d/mod_deflate.conf"

Do the same for dynportal-ssl.conf

This next set of instructions is from BVD in our Skype group:

1st step is only for apache error user’s

1st step
simple go to /etc/apache2/conf.d/ and rename all that files which is on .old like before /etc/apache2/conf.d/mod_deflate.conf.old
change into this mod_deflate.conf only and do same process on all files just remove .old or .bak some thing

2nd step
cd /usr/src/astguiclient/trunk
then run perl install.pl
install.pl will help you to create agi-bin missing files

3rd

rm -r /var/lib/asterisk/sounds
ln -s /usr/share/asterisk/firmware /var/lib/asterisk/firmware
ln -s /usr/share/asterisk/images /var/lib/asterisk/images
ln -s /usr/share/asterisk/moh /var/lib/asterisk/moh
ln -s /usr/share/asterisk/mohmp3 /var/lib/asterisk/moh
ln -s /usr/share/asterisk/sounds /var/lib/asterisk/sounds
ln -s /usr/share/asterisk/static-http /var/lib/asterisk/static-http
ln -s /usr/share/asterisk/phoneprov /var/lib/asterisk/phoneprov

ln -s /var/lib/asterisk/agi-bin /usr/share/asterisk/agi-bin
ln -s /var/lib/asterisk/phoneprov /usr/share/asterisk/phoneprov


image 101361114 15620149

You can also check out the video version from Innovate IT Lab

If you have any questions feel free to join our discord: https://discord.gg/ymGZJvF6hK

Chris aka carpenox

image 101361114 14092462

How to – Use the full functionality of the ViciDial installer by carpenox

CyburDial Installer

How to – Use the full functionality of the ViciDial installer by carpenox

Vicidial administrators, take note: the Carpenox Auto Installer is about to change the game. This tool transforms the usually complex setup of Vicidial into a smooth, hassle-free experience. Let me go over some post installation steps and key things to take note of and changes I suggest you make after the fact of using the installer. I will give you a few steps to do first:

This assumes you have installed already through this article: How to – Install Vicidial on Alma Linux 9 with my new auto installer

image 101361114 15620149

Step 1 – Login to the admin GUI and change the default password

After you reboot the server, which should only be done once you have attached the FQDN(Fully Qualified Domain Name) for the SSL cert in the very last step of the installation process. This step is important and I advise you don’t skip it if you plan to use webphones that are built into the installer. If you do skip this step, make sure you turn the firewall off before trying to run it post the initial install or certbot wont be able to get through to create the SSL. The command is “service firewalld stop” and then start it back again after you install the SSL. This being said, then login to that domain in your browser. For example: https://my.dialer.one (Use your domain this is NOT real)
The default login is 6666 and password 1234 – make sure you change this password and then go into users and give yourself all the permissions possible.

If you do decide to not use webphones and can not or will not be installing SSL, you will need to login still through the https port with https://192.168.1.1 (your IP) and change the password the same. You will need need to add the http port to your trusted zone as well as the dynamic portal non SSL port to public which is 81. You can do so with the following commands:

firewall-cmd --permanent --add-port=81/tcp
firewall-cmd --add-service=http --zone=trusted --permanent
firewall-cmd --reload

Step 2 – Lock the firewall down

Hackers these days are quick, like I mean I have had servers provisioned from well known hosting companies like Hetzner, Vultr, DigitalOcean, OVH Cloud, IONOS, Contabo and many others within 15 minutes. They scan these known IP ranges and go for known vulnerabilities very quick and will install rootkits, crypto miners, DDOS bots and other malware. The firewall rules I have set in place leave the needed ports to be open to use the dialer in the “trusted” zone, however I have left port 443(https) open to public zone so you can login and change the default password, because you can not use the dynamic portal to validate your IP until after the default password has been changed.

So, now that you’ve changed that password, lets remove the https port 443 from the public zone. To do so type the following commands: You can also see more use for the firewall here: How to – Use Firewalld via command line

firewall-cmd --permanent --remove-service=https
firewall-cmd --reload

You also need to update the dynamic portal redirect link with this command:

nano /var/www/vhosts/dynportal/inc/defaults.inc.php

Change the https://cyburdial.com/agc/cyburdial.php to https://yourdomain.com/agc/vicidial.php

Dynamic Portal settings

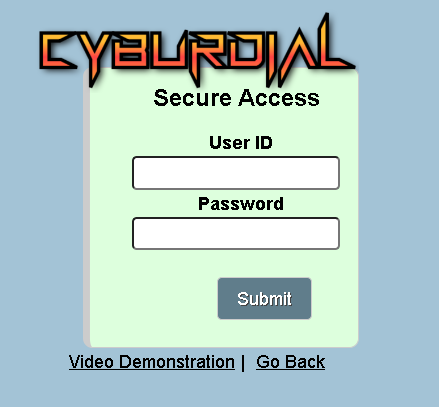
You should not be able to get to your domain at this point, you will need to use the dynamic portal login to validate your IP. You can find the URL for this at https://my.dialer.one:446/valid8.php (Again, use your domain) or for those of you that are only using IP – http://192.168.1.1:81/valid8.php. When you go to that page you will see a login area that looks like the image below:

Dynamic Portal

If you have followed the previous steps you should now be redirected to the ViciDial agent page to login with your username and password. Just browse to the admin area by removing the /agc/vicidial.php part. Some more advanced steps would be to change the Dynamic portal port off of 446 to something above the 50000 range as it takes more time for hackers to scan this high and they typically will not waste the time. Changing the name of the valid8.php file is also a good standard operating procedure to put in place, however this take some other changes in the template file as well, that I will not go over on this article. If you would like to see an article for that, post a comment below.

Contabo opens DC in Singapore

Step 3 – Setup your ViciDial instance

At this point, most of you should know how to setup your your Vicidial configurations and setup. If not make sure to check out a few of my friends YouTube pages with lots of content regarding this:

If you do decide to use the standard-db.sh file on my github, there is one thing that I messed up on the original design that needs to be fixed post import. Adding an “a” to the phone login on each user account. To run the standard-db file which comes pre-configured with everything ready to go other than adding DID’s and your VoIP carrier IP, simply run the commands below:

cd /usr/src/vicidial-install-scripts
chmod +x standard-db.sh
./standard-db.sh

Once you use this file, your new password to get into the 6666 user will be “CyburDial2024”

After this go into each user account an add the letter “a” to the phone login area as shown below:

User Account

Step 4 – Change domain from mine to yours

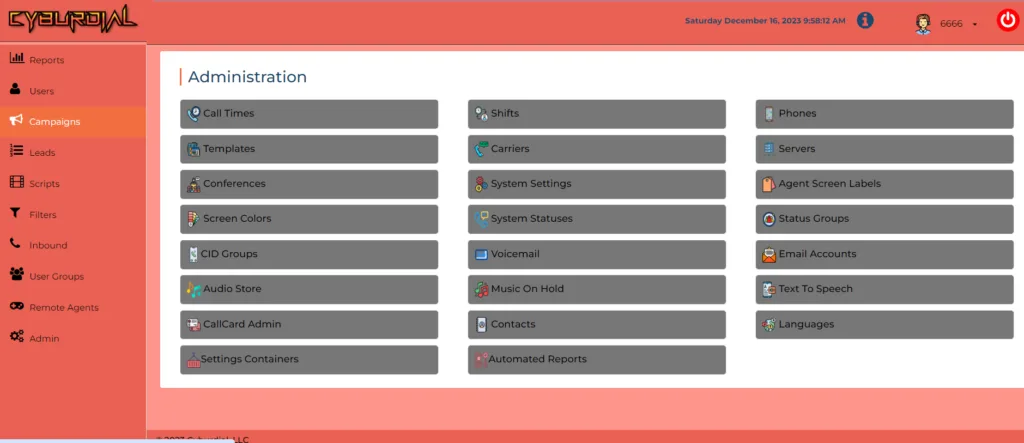
The first place you need to change the domain from mine to yours is in the server itself for the websocket location in admin > servers as shown below:

WSS socket

The second place is in the webrtc template labeled as “SIP_generic” in admin > templates as shown below:

webrtc template

The last place in in system settings for the audio store or “sounds web server” location as shown below:

sounds web server
image 101361114 14092462

Step 5 – Create audio store directory when using the standard DB file

cd /var/www/html
mkdir hgcjvmrjzqcngw47wf5zf4xjzd9n0k
chmod -R 755 hgcjvmrjzqcngw47wf5zf4xjzd9n0k
chown -R apache:apache hgcjvmrjzqcngw47wf5zf4xjzd9n0k
cp -R /var/lib/asterisk/sounds/* /var/www/html/hgcjvmrjzqcngw47wf5zf4xjzd9n0k

Step 6 – Add DID’s and Carrier IP

This next step is going on the thought of using the standard-db file on my github, but for those of you that do the config’s yourself, don’t forget the bulk tools area is a great way for adding your DID’s in bulk.

Admin Utils

The next step is to add your DID’s, you can do so easily through the bulk tools in Admin > Reports > admin utilities

After this go Admin Bulk Tools

Click the highlighted area and the first area you see will be to copy DID’s, select the one I have there that says Copy this DID as shown below and paste your DID’s in the area available, then click submit.

Bulk Tools
Copy DID's

Paste them in this box and click submit

The second part of this is to change the carrier IP in admin > carriers > carrier

Carrier IP change

That’s it, you can start dialing. Now lets go over a few tools I have added to help manage and debug your systems:

  • sngrep – a command-line tool used for capturing and analyzing SIP (Session Initiation Protocol) packets
  • htop – an interactive system monitor and process viewer for Unix system
  • iftop – a similar tool used for the network card interface
  • postfix – a free and open-source mail transfer agent (MTA) that routes and delivers email
  • dovecot – an open-source IMAP and POP3 email server for Unix-like operating systems
  • roundcubemail – a web based GUI for email
  • inxi – detailed hardware information (inxi -Fxz)

Hopefully this helps with some of the questions I have been asked and common issues people run into. If you have any other questions, feel free to join my discord channel: https://discord.gg/ymGZJvF6hK or comment below.

Chris aka carpenox

How to – Decrease SDP(short duration percent) in ViciDial

Short Duration Percent

How to – Decrease SDP(short duration percent) in ViciDial

There is a new feature in ViciDial as of SVN 3878 that will allow you to increase the call handle time through the AMD system which would lower your Short Duration Percent(SDP) in your carrier stats. Doing so can typically save you hundreds if not thousands per month in VoIP fees for being below their SDP requirements. Adding one line to you carrier dialplan as show below will do this for you. Doing so will also save your DID’s (Caller ID’s).

Short Duration Percent

This example will add 7 seconds to each call.

exten => _8567.,1,AGI(agi://127.0.0.1:4577/call_log)
exten => _8567.,n,Set(__AMDMINLEN=7)
exten => _8567.,n,Dial(SIP/carrier/${EXTEN:4},,tToR)
exten => _8567.,n,Hangup

I hope this helps

-Chris aka carpenox

August 2024 VICIdial Security Update

Security Update needed

August 2024 VICIdial Security Update

Please read this carefully as it contains important information regarding the security of your VICIdial system.

The ViciDial Group recently conducted a security audit of VICIdial which resulted in the identification of severe vulnerabilities. We have patched these and submitted these changes to the code-base. Any system that is at SVN version 3848 or greater already has them. If your system is below that version, we strongly recommend that you upgrade to address these concerns. If you would like us to upgrade your system for you, please send a new email to support@cyburdial.com and put “Security Upgrade” in the subject. A typical upgrade takes about 15 to 30 minutes of support time. You can see the seriousness of these exploit here: https://packetstormsecurity.com/files/181461/VICIdial-2.14-917a-Remote-Code-Execution.html
https://packetstormsecurity.com/files/181460/VICIdial-2.14-917a-SQL-Injection.html

To find the SVN version of your VICIdial installation, log into your administator account and go to “Admin”, then click on “System Settings”. It will be the second line from the top, on the right, under “SVN Version”.

Please note, if your setup contains customizations done directly to VICIdial’s code, further review of your system will be needed as it may not be possible to upgrade you.

image

You can update your SVN by following this article: How to – Update your Vicidial version with subversion

Chris aka carpenox