PHP2Shell: Critical PHP Remote Code Execution Vulnerabilities Require Immediate Action
The PHP community has released emergency security updates to address two critical remote code execution vulnerabilities, CVE-2026-109618 and CVE-2026-109619, collectively being referred to as PHP2Shell. Both vulnerabilities can allow an unauthenticated attacker to execute code on affected web servers through specially crafted HTTP requests. PHP has rated both vulnerabilities as 9.2 (Critical) and administrators should patch immediately. [almalinux.org], [almalinux.org]
The vulnerabilities affect multiple PHP versions and deployment methods, including PHP-FPM, Apache mod_php, CGI, LiteSpeed, and FrankenPHP installations. PHP released fixed versions on October 21, 2026, with updates available in:
- PHP 8.2.35
- PHP 8.3.36
- PHP 8.4.27
- PHP 8.5.12
[almalinux.org], [phpvulnera…lities.app]
ViciBox 11 and ViciBox 12
The ViciDial team has already published fixes for supported ViciBox releases.
ViciBox 11
Documentation:
Update commands:
zypper ref
zypper dup --from openSUSE-Leap-15.5-ViciDial-ViciBox --allow-vendor-change
systemctl restart apache2
After updating, verify PHP:
php -vYou should see:
PHP 7.4.34-dev
ViciBox 12
Documentation:
Update commands:
zypper ar https://download.opensuse.org/repositories/devel:/languages:/php:/php82/openSUSE_Leap_15.6/devel:languages:php:php82.repo
zypper mr -f devel_languages_php_php82
zypper --gpg-auto-import-keys ref
zypper dup --from devel_languages_php_php82 --allow-vendor-change
systemctl restart apache2
After updating, verify PHP:
php -vYou should see:
PHP 8.2.35 or later.
Important Note for ViciBox 11 Users
The ViciDial team has indicated that it is becoming increasingly difficult to maintain and build packages for the aging ViciBox 11 platform. Administrators still running ViciBox 11 or older should begin planning an upgrade path, as older openSUSE repositories may eventually be removed from public mirrors.
AlmaLinux Fix
AlmaLinux has released patched PHP packages for all supported PHP streams across AlmaLinux 8, 9, and 10. The AlmaLinux project confirmed that patched packages are now available in the production repositories. [almalinux.org]
To update:
sudo dnf clean metadata
sudo dnf upgrade 'php*'
Restart PHP-FPM:
sudo systemctl restart php-fpmIf you are using Apache with mod_php:
sudo systemctl restart httpdVerify the installed version:
php -vFor systems running PHP 8.2, the patched version should be:
PHP 8.2.35
or newer. AlmaLinux has also backported protections for some older, end-of-life streams where possible. [almalinux.org], [computingf…rgeeks.com]
Rocky Linux Fix
Rocky Linux administrators can patch affected systems using the standard AppStream update process. Updated packages have been synchronized from Red Hat’s security advisories for supported PHP streams. [computingf…rgeeks.com]
Update PHP:
sudo dnf upgrade 'php*'Restart services:
sudo systemctl restart php-fpm
sudo systemctl restart httpd
Verify:
php -vSupported streams should be updated to patched package releases, including PHP 8.2.35 and PHP 8.3.36 where applicable. [computingf…rgeeks.com], [php2shell.app]
Special Notice for VICIdial Servers Running PHP 7.4
Many older VICIdial deployments on AlmaLinux 8, Rocky Linux 8, and ViciBox 11 continue to use PHP 7.4. While the upstream PHP project no longer maintains the 7.4 branch, several distributions have backported security fixes to their packaged versions. The PHP2Shell vulnerabilities have been patched in supported vendor repositories even though the version number may still report as PHP 7.4.x. Administrators should not assume they are protected simply because they are running PHP 7.4 and should verify that all available operating system updates have been installed. [computingf…rgeeks.com], [php2shell.app]
AlmaLinux PHP 7.4
Update all PHP packages:
sudo dnf clean all
sudo dnf upgrade 'php*'
sudo systemctl restart httpd
Verify installed packages:
rpm -q php-commonphp -vAlmaLinux has released patched packages for PHP 7.4 in its repositories, including backported fixes for the PHP2Shell vulnerabilities. [computingf…rgeeks.com], [almalinux.org]
Rocky Linux PHP 7.4
Update all PHP packages:
sudo dnf clean all
sudo dnf upgrade 'php*'
sudo systemctl restart httpd
Verify package versions:
rpm -q php-commonphp -vRocky Linux has synchronized the corresponding security updates from Red Hat for supported PHP 7.4 streams. Because Red Hat backports security fixes, the displayed version number may not change significantly even though the vulnerability has been patched. Administrators should review package changelogs and installed RPM versions rather than relying solely on php -v. [computingf…rgeeks.com], [php2shell.app]
Verify Your System Is Patched
After updating, verify your installed PHP packages:
rpm -q php-commonOr review the package changelog:
rpm -q --changelog php-common | grep CVEIf your repository updates are current and the CVE references appear in the changelog, the PHP2Shell fixes have been applied even if the PHP version string still shows 7.4. [php2shell.app]
IMPORTANT: PHP 7.4 is officially end-of-life upstream. While AlmaLinux, Rocky Linux, and ViciBox may provide backported security fixes, organizations should develop a migration plan to PHP 8.2 or newer as soon as practical for long-term security and support. [computingf…rgeeks.com], [almalinux.org]
What Administrators Should Do Right Now
- Identify all servers running PHP.
- Update PHP packages immediately.
- Restart PHP-FPM and/or Apache after patching.
- Verify the running version.
- Review logs for suspicious requests dating back to October 2026.
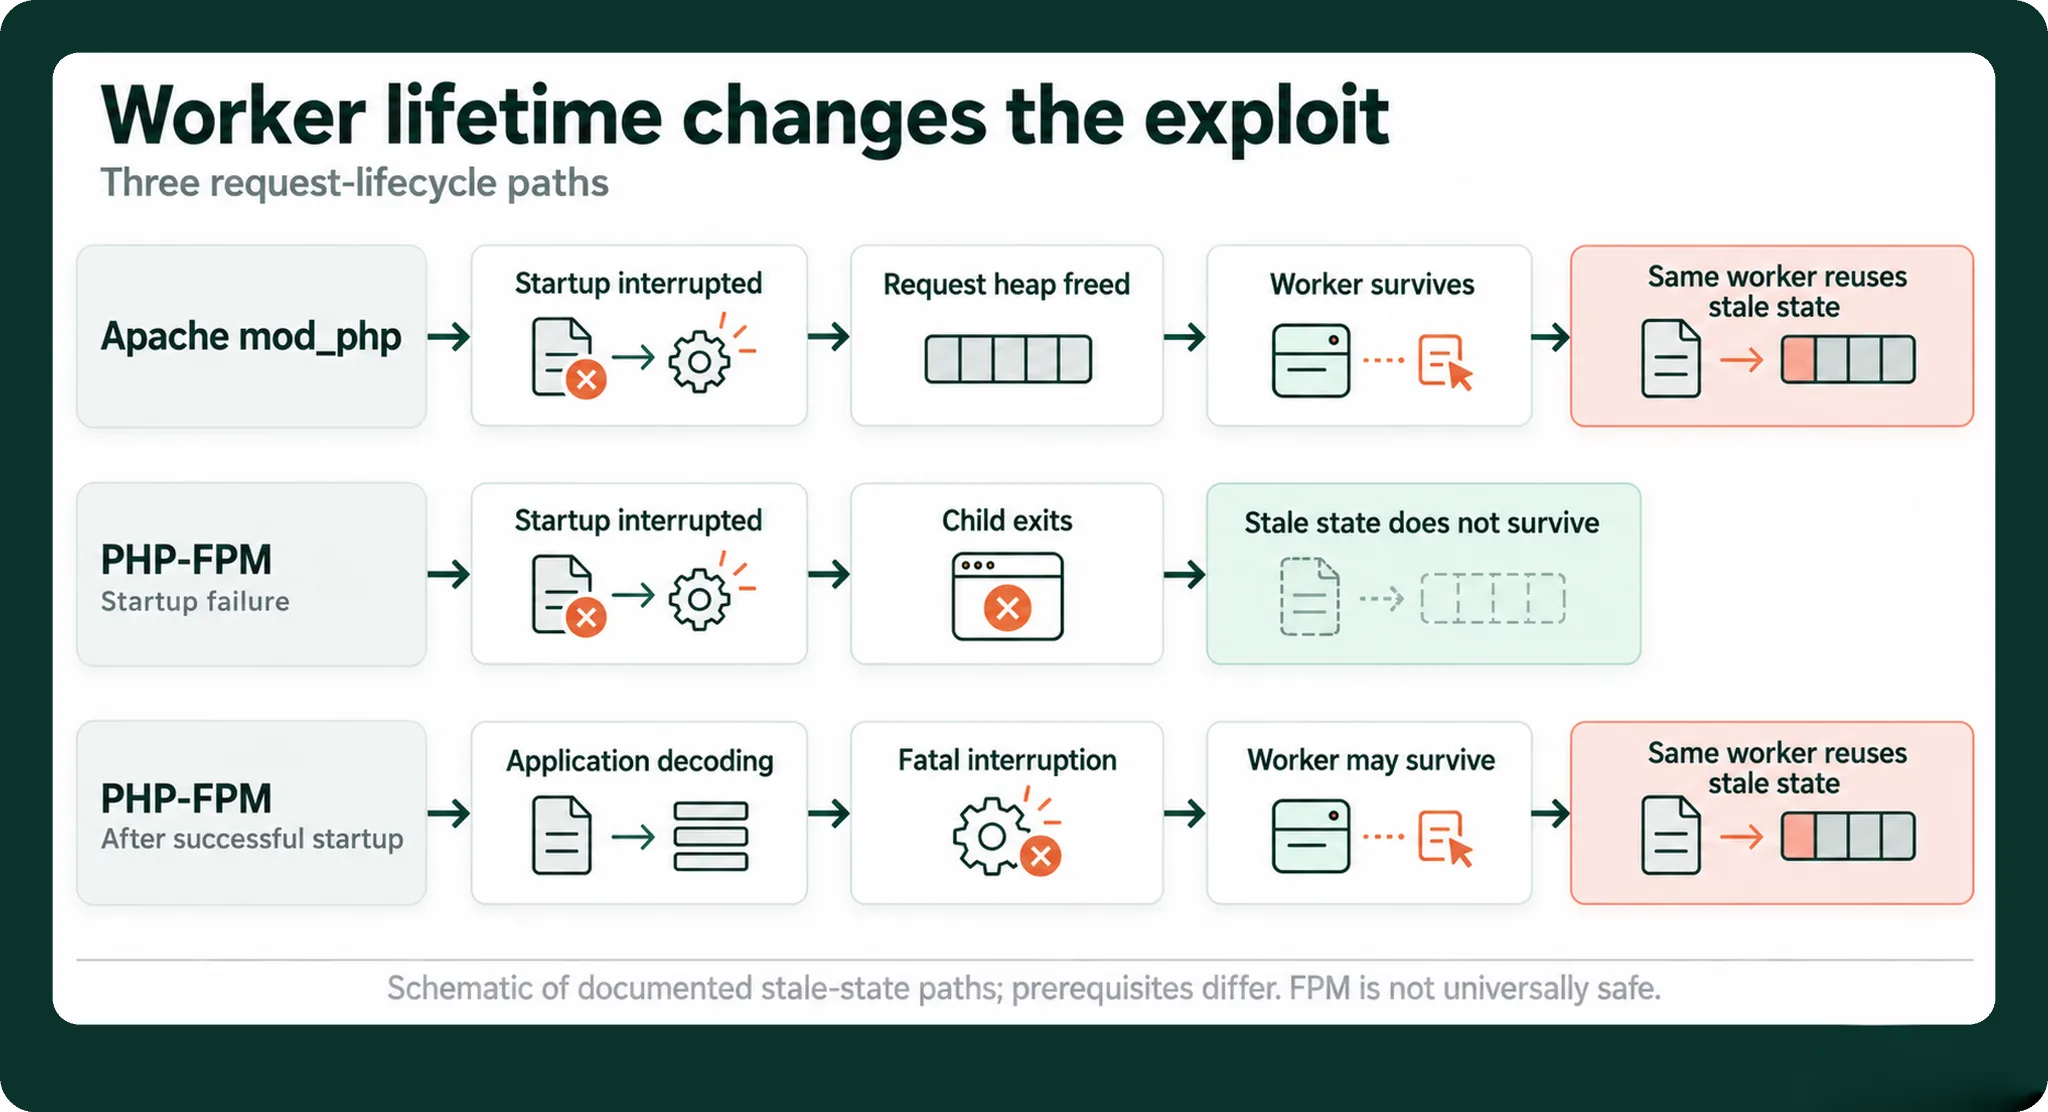
- Prioritize systems using Apache mod_php, as PHP developers have identified them as the highest-risk deployment model. [hackread.com], [notebookcheck.net]
Final Thoughts
Unlike vulnerabilities that affect a specific CMS or plugin, PHP2Shell targets the PHP runtime itself. This means WordPress, Laravel, Drupal, Joomla, VICIdial, custom applications, and virtually any PHP-powered application may be exposed if the underlying PHP installation remains unpatched. The safest course of action is simple: update PHP immediately and verify that your services have restarted successfully. [almalinux.org], [phpvulnera…lities.app]
Chris aka carpenox